
Threat intelligence, productized
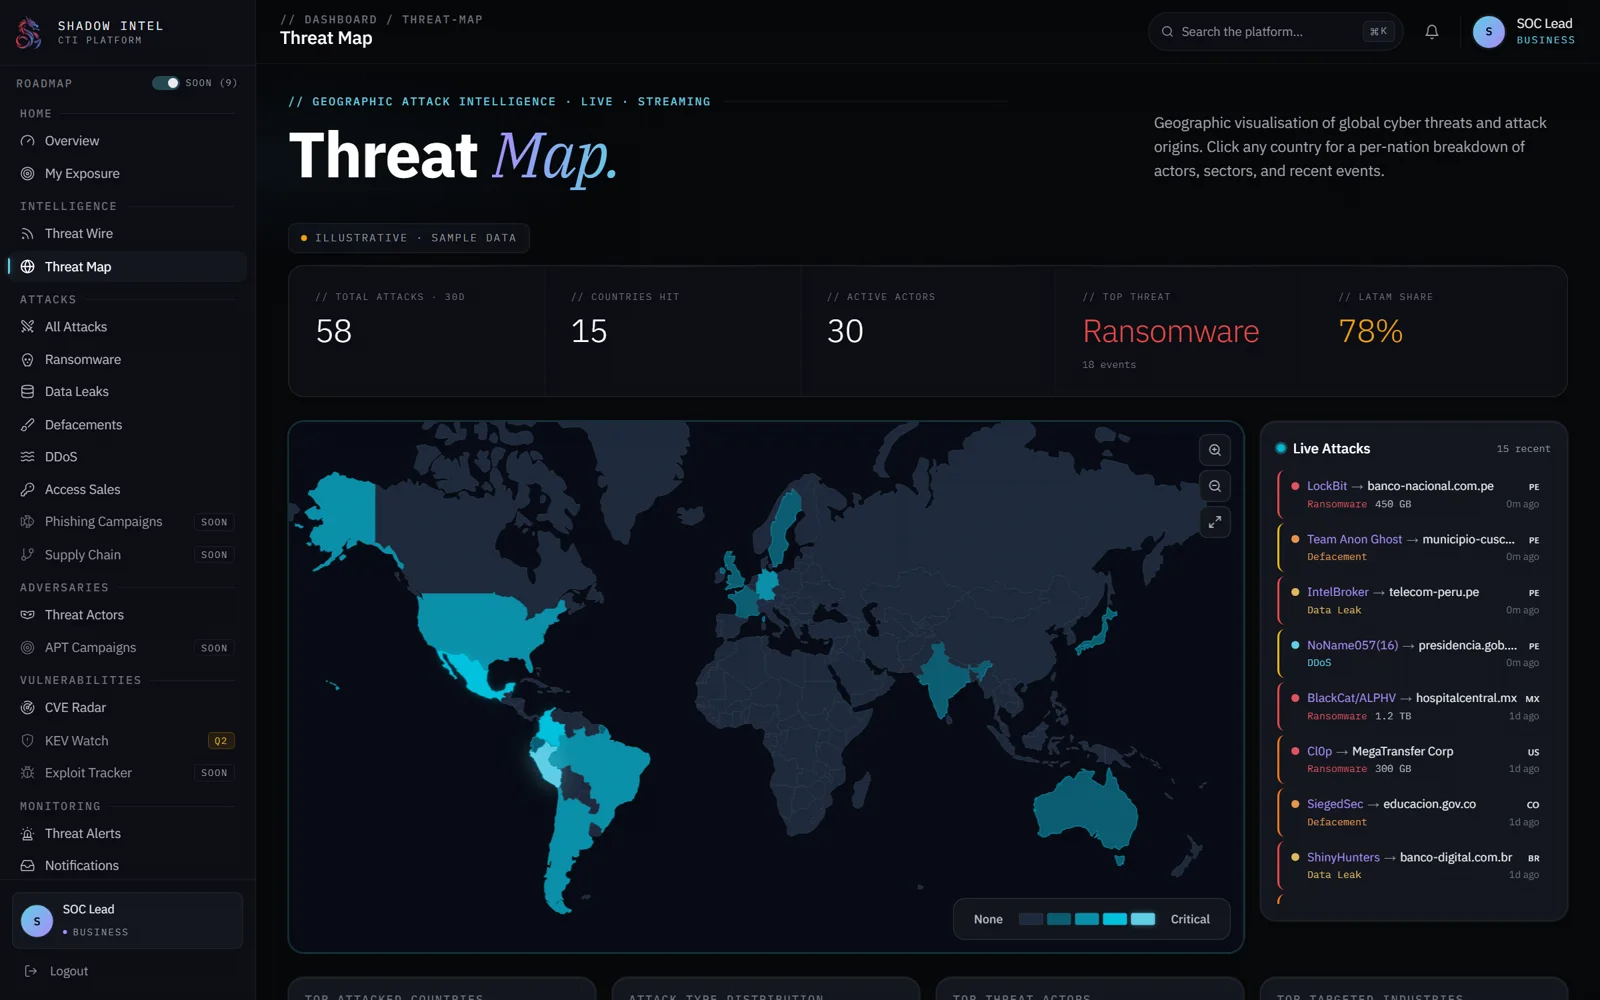
Our services surface the underground data; our products turn it into actionable intelligence, available 24/7. Starting with Shadow Intel, coming soon.
Shadow Intel
Threat intelligence, mapped to your attack surface.
A Cyber Threat Intelligence SaaS platform: up-to-the-minute feeds, dark web monitoring, and native coverage of the Latin American underground. Verified IOCs, tracked actors, and correlated attacks. All in a single pane of glass.
- Native coverage of the Spanish- and Portuguese-language underground
- Verified IOCs with deduplication and confidence-based decay
- Monitoring of BreachForums, Telegram, ransomware.live, and defacements
- Dual authentication (session + API key) and plan-based access control
Shadow Academy
Elite training with custom-built labs.
Certification prep with custom labs (OSCP, CPTS, CRTO, and more), tailored CTFs for companies and events, and role-based bootcamps. All led by operators with real hours in the field.
- Custom certification prep labs
- Custom CTFs (corporate · events · recruiting)
- Offensive, defensive, and cloud bootcamps
- Content localized for LATAM
Shadow Feeds
Machine-readable IOC feeds for your stack.
An API of verified indicators (STIX/TAXII, JSON, CSV) that feeds straight into your SIEM, TIP, or EDR. A sister product to Shadow Intel, built for programmatic integration.
- STIX / TAXII 2.1
- IOC Vault with confidence scoring
- Webhooks and pull API
- Data freshness SLA
Shadow Leaks
Underground monitoring and digital risk protection.
Monitoring for leaked credentials, data exposure, brand impersonation, and mentions across underground forums and marketplaces. Backed by an integrated takedown service.
- Leaked credentials and data
- Brand protection / anti-phishing
- Dark web monitoring
- Operationalized takedowns
Modules on the way
AI & LLM Red Teaming
SoonBreak your AI before the internet does: prompt injection, jailbreaks, and agent abuse, mapped to the OWASP LLM Top 10.
Automated Takedown
SoonFrom Shadow Intel alert to phishing site offline: impersonations and leaked data taken down, fast.
CTEM · Continuous Threat Exposure Management
SoonGartner's framework, put into practice: scoping, discovery, prioritization, validation, and mobilization, on a continuous cycle.
Deception as a Service (Honeypots)
Seed your network with traps that turn attacker curiosity into an early-warning siren.
Supply Chain Security
Know your vendors' risk before it becomes your breach. SBOM analysis and third-party monitoring.
Bug Bounty Management & Triage
Run a crowdsourced program without drowning in it: we triage, validate, and route every report.
OSINT as a Service
On-demand investigations, due diligence, and executive exposure mapping from open and closed sources.
Cyber Range & Training
Live-fire environments where your blue team battles real-world scenarios, with content localized for LATAM.
Executive Protection & Anti-Deepfake
Monitor and defend your leadership against impersonation, deepfakes, and doxxing.
Quantum Readiness
Inventory your cryptography and chart your path to post-quantum before "harvest now, decrypt later" catches up with you.